· Right On Tech · Security Guides & Updates
Ransomware: The First 60 Minutes — A Response Plan for Small Businesses
Ransomware rarely announces itself politely. Someone calls out that their files have strange extensions, a note appears on the screen demanding payment, or the shared drive suddenly will not open. What you do in the next hour can decide whether you lose a day or a month.
This plan is written for small businesses without a security team. It follows the response checklist in CISA's #StopRansomware Guide, translated into steps an office manager can take while help is on the way. Print it now, while things are calm.
Why the first hour matters
Ransomware spreads from machine to machine across your network, and many attacks also try to reach backups and cloud accounts. Every minute a connected computer stays online gives it more chances to encrypt shared folders. Quick, calm containment limits how much has to be rebuilt, protects the backups you will restore from, and keeps the evidence your insurer and investigators need. The steps below are in rough order, but if you have two people, do some of them in parallel.
Signs you may be dealing with ransomware
- Files that will not open, or have new, odd file extensions
- A ransom note as a text file, web page or desktop wallpaper
- Shared drives or the server suddenly unreachable or very slow
- Antivirus alerts on several computers at once
- Unknown admin accounts or remote-access tools you did not install
Minutes 0–5: Stop the spread
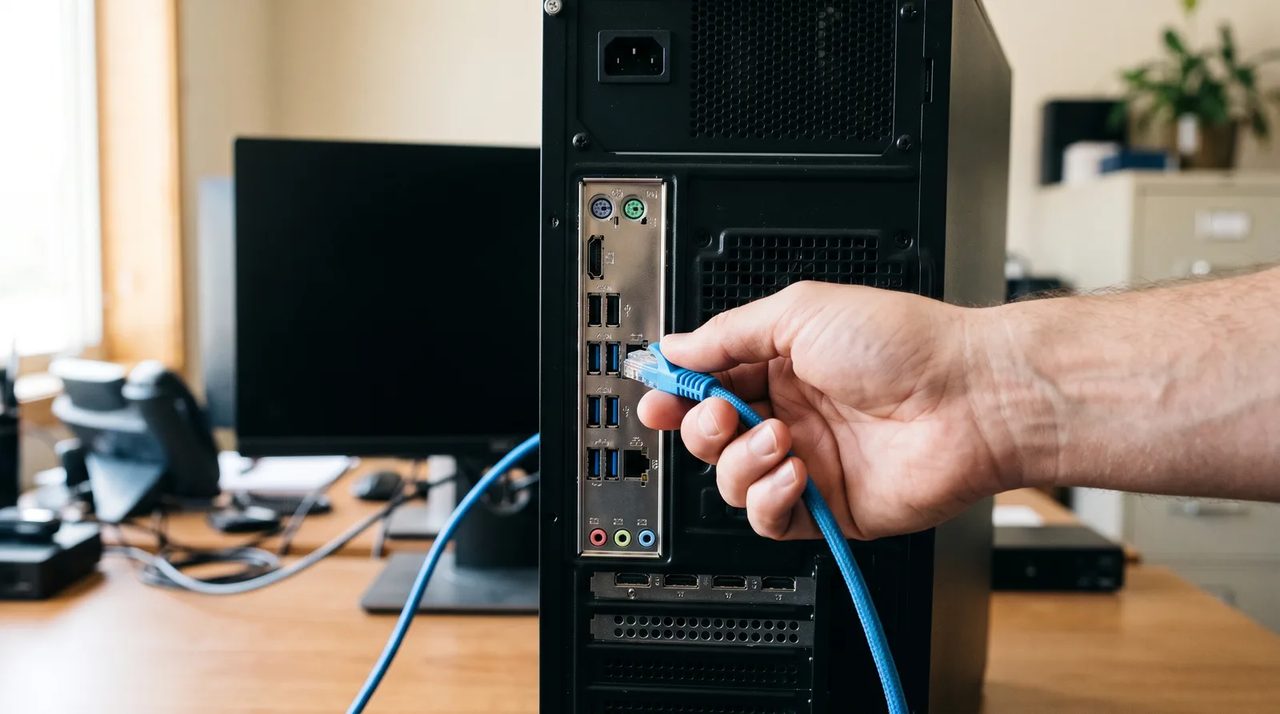
- Disconnect affected computers from the network. Unplug the network cable and turn off Wi-Fi. If several machines or the server are affected, disconnect the internet connection or the main network switch.
- Do not turn computers off unless you cannot disconnect them. CISA advises powering down only if you cannot take the network down, because shutting down erases evidence held in memory that investigators may need.
- Take photos of the ransom note and any error messages with a phone.
- Do not delete files, wipe machines or run cleanup tools yet. You may destroy the evidence and the data you need to recover.
Minutes 5–15: Get the right people involved
- Call your IT provider or internal IT contact. Use phone calls or text messages, not company email or Teams. CISA recommends out-of-band communication so the attackers do not learn they have been spotted.
- Name one person in charge of decisions and one person to keep notes. Too many people making changes at once causes damage.
- Tell staff to stop using their computers and not to plug in USB drives or reconnect anything until told.
Minutes 15–30: Protect backups and accounts
- Disconnect backups. Unplug external backup drives and isolate the backup appliance or NAS. Ransomware often goes after backups first.
- Check cloud sync. OneDrive and similar tools may be syncing encrypted files to the cloud. Pause syncing on affected PCs. Microsoft 365 lets you restore a OneDrive to an earlier point within the last 30 days, but only start that once the infection is contained.
- Secure key accounts from a clean device. Using a computer or phone that was not affected, have your IT contact reset passwords for administrator and email accounts, sign out all sessions, and look for admin accounts that should not exist.
- Shut off remote access. CISA recommends disabling exposed services such as VPN and remote desktop that attackers could use to get back in.
Minutes 30–45: Make the outside calls
- Cyber insurance: if you have a policy, call the claims line now. Many policies require prompt notice and may require you to use their approved response firms. Starting work with an outside vendor first could complicate a claim.
- Law enforcement: report to the FBI through ic3.gov or your local FBI field office, and to CISA at cisa.gov/report. Reporting can help investigators, and CISA advises consulting law enforcement about possible decryptors.
- Legal counsel: if customer or employee personal data may have been taken, talk to a lawyer about notification duties. In California, for example, a 2025 amendment to Civil Code 1798.82 requires notifying affected residents within 30 calendar days of discovering a breach, with limited exceptions.
Minutes 45–60: Take stock and plan
- List what is affected: which computers, servers, shared drives and cloud accounts.
- List what still works: phones, Microsoft 365 email on unaffected devices, line-of-business apps in the cloud.
- Check your backups: when did the last good backup run, and is it untouched?
- Decide how the business keeps running today: paper forms, phones, a temporary laptop on a separate network.
- Agree on what to tell staff and customers, and who says it. Keep it factual and brief.
Things not to do
- Do not contact the attackers or pay on your own. Payment does not guarantee you get your data back, and the U.S. Treasury's Office of Foreign Assets Control has warned that ransomware payments can carry sanctions risks. Any discussion of payment belongs with your insurer, lawyer and law enforcement.
- Do not restore from backup onto infected machines. The ransomware or the attacker's access may still be there.
- Do not reconnect machines "to see if it's fixed".
- Do not wipe everything right away. Evidence helps find how the attackers got in, so you can close that door.
After the first hour
Recovery is a longer process, usually led by your IT provider or an incident response firm. Following CISA's checklist, it typically includes finding how the attackers got in, removing their access, rebuilding affected systems from clean images, restoring data from offline backups in priority order, resetting passwords, and patching the weakness they used. Only clean, rebuilt systems should rejoin the network.
Once things are running again, hold a short review while the details are fresh:
- How did the attackers get in, and is that path now closed?
- How long did the restore take compared with what the business can tolerate?
- Which contacts, passwords or instructions were missing when you needed them?
- What will you change: MFA, backups, patching, training or monitoring?
Prepare your one-page plan today
The best time to fill this in is now. Keep a printed copy somewhere you can reach without a computer:
| What | Fill in |
| IT provider emergency number | |
| Person in charge during an incident (and backup person) | |
| Cyber insurance claims line and policy number | |
| Lawyer | |
| Bank fraud line | |
| Where backups are and how to disconnect them | |
| How to shut off the internet connection |
Pair the plan with the basics that prevent most attacks: MFA on every account, updates installed promptly, offline or immutable backups that are tested, and staff who know to report anything odd right away.
Get a plan in place
Nobody wants to think about ransomware, but an hour spent preparing can save weeks. Right On Tech helps small businesses write a simple response plan, set up protected backups, and keep systems patched and monitored through our managed IT service.